When someone falls for an online scam, an inevitable question comes up: where does data stolen through phishing actually go? People tend to assume that criminals are only after a quick payout, but the reality is very different. The data becomes part of a parallel market where it circulates, gets resold and is used for new fraud schemes for years.
How is data collected in a phishing attack?
Phishing sites usually imitate real pages, from banks to delivery companies. They may look legitimate, but their only purpose is to obtain personal information.
Common data capture methods
- Fake forms: They ask for names, addresses, passwords or banking information.
- Misused legitimate services: Forms on well-known platforms that redirect the information to the attacker.
- Panels or messaging bots: The collected data reaches the criminals immediately thanks to automated systems.
Once the victim submits their information, it lands in the attackers' hands almost instantly.
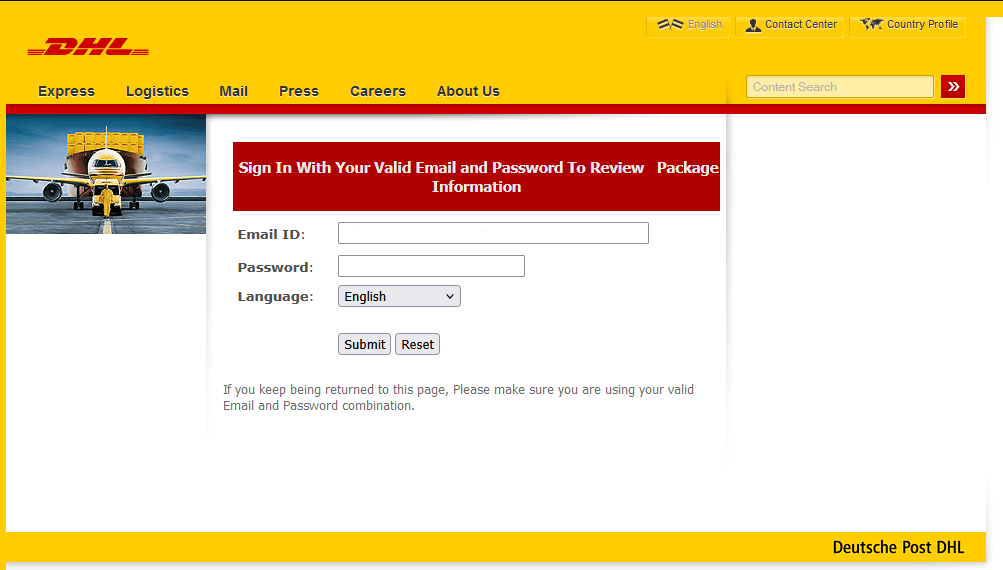
A fraudulent DHL page asks users to enter the username and password of their legitimate DHL account.
What kind of data are cybercriminals after?
Scammers are not only looking for passwords or card numbers. Their interest covers a wide range of information useful for more elaborate fraud.
Personal data
Full names, phone numbers, email addresses or physical addresses. With this they can personalize scams and make them more believable.
Sensitive documents
Scans of ID cards, driver's licenses or tax identification numbers. These are key for identity theft or fraudulent loan applications.
Credentials
Usernames, passwords and verification codes.
Biometric data
Faces, fingerprints or voice samples that can be used to generate digital forgeries.
Financial information
Bank cards or access to digital wallets.
Almost any piece of data has value on the underground market, whether for direct scams or to be resold later on.
Where does data stolen through phishing actually go?
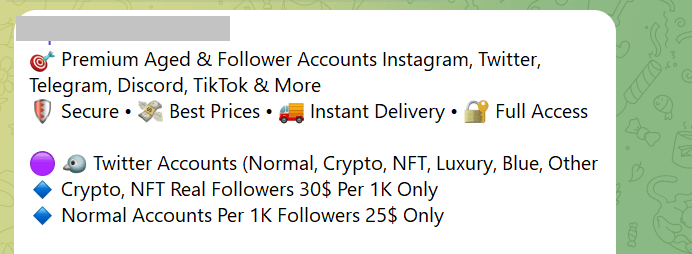
An ad promoting the sale of social media account credentials on Telegram
Once stolen, the information follows a path that rarely ends with a single attacker. More often than not, it passes through different hands and is reused in multiple fraud schemes.
1. Bulk sale of raw data
The data obtained is bundled into enormous files and sold to the highest bidder.
These packages typically mix useful information, outdated data and junk. That is why their initial price is relatively low.
2. Sorting and verification
Whoever buys these files reviews the information to separate what is useful from what is worthless.
They check whether the passwords work or whether they match previously leaked data.
The result is a digital dossier ready to be used in new attacks.
3. Resale at a higher value
Once organized and verified, the data is sold again, this time at a higher price.
These sales happen both on the dark web and in messaging apps.
The more complete and recent the information is, the higher its value.
3. New personalized attacks
With the dossiers ready, criminals can:
- Send personalized emails impersonating bosses, family members or official institutions.
- Access social media accounts and use personal information for blackmail.
- Use compromised accounts to send out new fraudulent links.
- Apply for credit or make purchases in the victim's name.
The cycle continues as long as the information remains profitable.
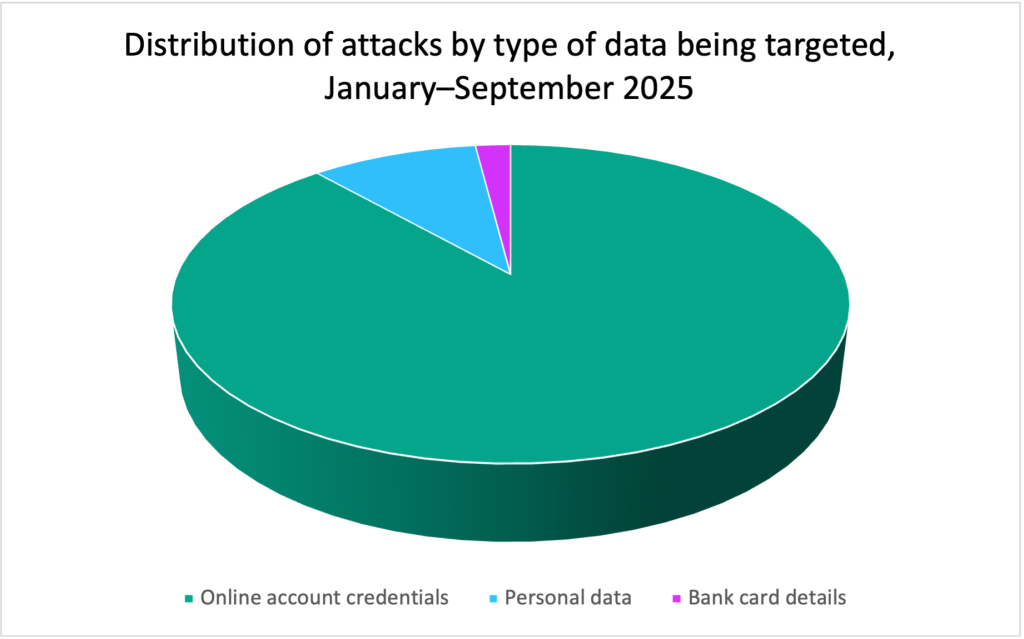
Distribution of incidents by category of compromised data, between January and September 2025.
What to do if your data has been stolen
If someone falls for a fake site, acting fast is key.
Immediate steps
- Contact your bank if financial data was handed over.
- Change passwords if the same password was used on other services.
- Close active sessions on important accounts.
- Turn on two-factor authentication (2FA), preferably with authenticator apps.
Preventive measures going forward
- Avoid reusing passwords.
- Use a password manager.
- Check senders and links before clicking.
- Keep security solutions that detect fraudulent sites switched on.
- Use secure authentication methods to reduce the risk of unauthorized access.
Prevention will always be the best defense against increasingly sophisticated fraud attempts.
How to protect yourself from phishing day to day
Simple recommendations
- Do not open suspicious links, even if they look urgent.
- Verify that the website domain is the official one.
- Avoid sharing sensitive information from emails or messages.
- Keep unique, strong passwords for every service.
- Use two-factor authentication on important accounts.
Digital security depends to a large extent on small everyday actions.
Data stolen through phishing does not disappear; it moves through an underground market where it can circulate for years. Understanding the path it follows helps us grasp the real value of our personal information.
Prevention, the right tools and attention to warning signs can make the difference between stopping fraud in time and becoming the victim of a chain of scams.